In 2026, enterprise server infrastructure is no longer dictated solely by compute power, latency, or bandwidth. It is dictated by the law. As international governments rapidly enact aggressive data localization regulations, multinational enterprises are finding that multi-tenant public clouds have transformed from flexible IT solutions into massive legal liabilities.
When you place highly sensitive intellectual property, financial records, or citizen data into a hyperscale cloud environment, you surrender physical control. Your data is sharded, replicated, and moved dynamically across geographic boundaries to optimize the cloud provider's network efficiency. With the enforcement of laws spanning from Europe and the UK to Brazil, India, and the Middle East, this lack of physical data isolation is unacceptable. Enterprise search trends are shifting heavily toward absolute data localization and sovereign architectures.
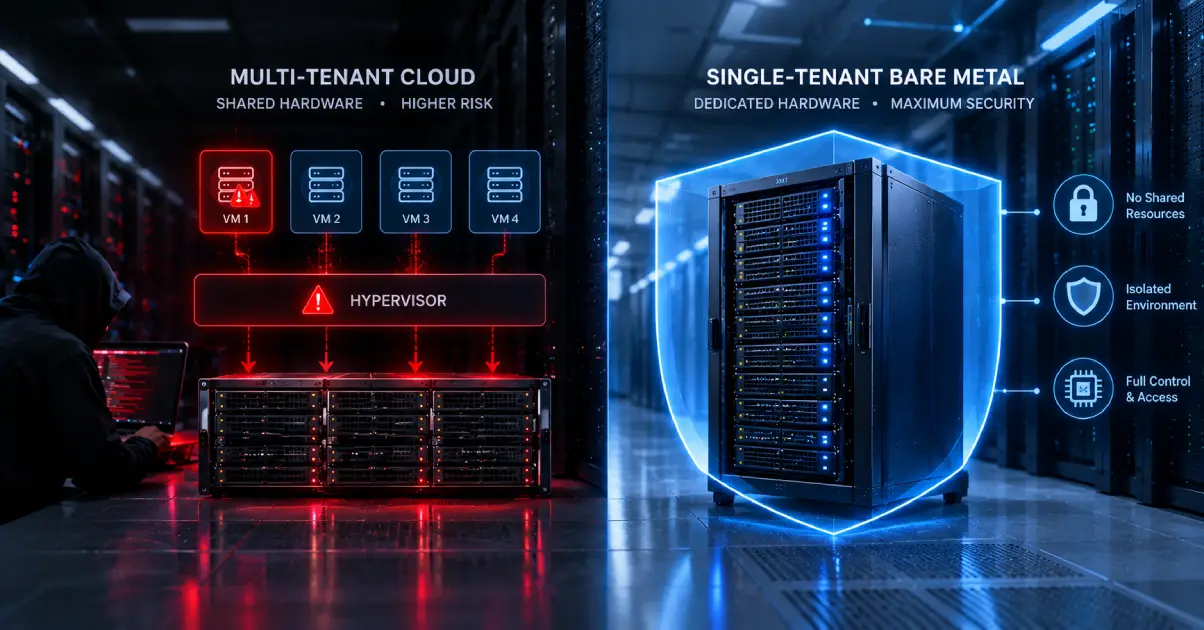
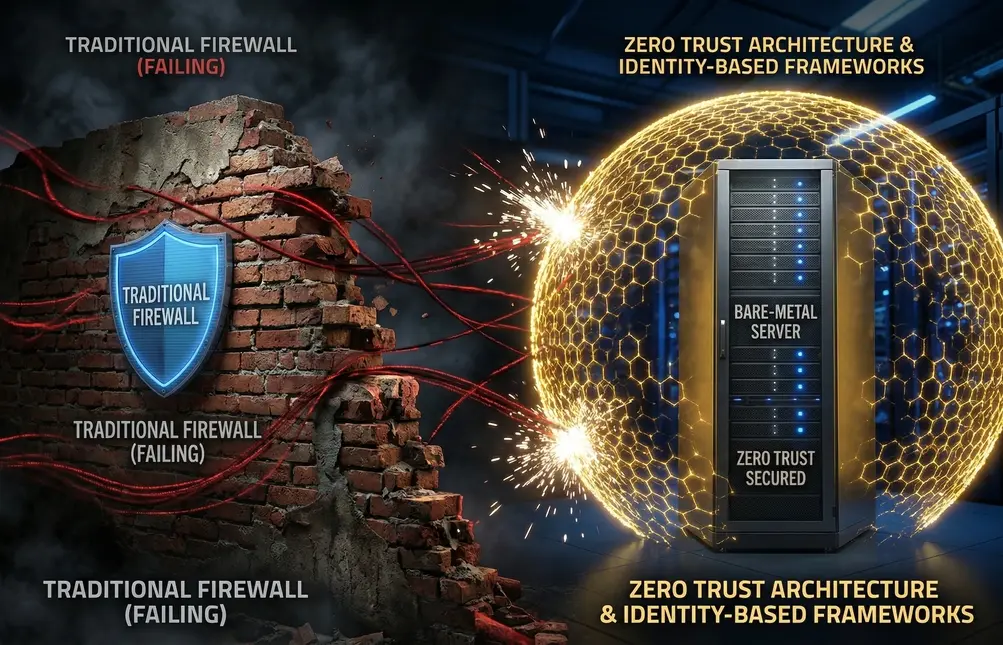
For Chief Information Security Officers (CISOs) and enterprise architects, the conversation has fundamentally shifted from technical specifications to global business risk mitigation. The most effective way to navigate the treacherous waters of worldwide data sovereignty is to bypass the shared environments of hyperscalers entirely. By deploying strictly isolated, single-tenant bare-metal servers in strategic regional data centers, multinational corporations can architect infrastructure that achieves total global compliance by design.
The Cloud Conflict: The US CLOUD Act vs. Global Privacy
To understand the legal necessity of bare-metal isolation, you must first understand the fundamental conflict governing the public cloud industry.
The vast majority of the world's cloud infrastructure is owned by United States-based corporations. Under the US CLOUD (Clarifying Lawful Overseas Use of Data) Act, US law enforcement agencies can compel these technology companies to hand over customer data, regardless of where in the world that data is physically stored. The CLOUD Act effectively bypasses traditional international agreements, such as Mutual Legal Assistance Treaties (MLATs).
The European Data Protection Board has made it clear that service providers subject to EU law cannot legally base data transfers to the US solely on CLOUD Act requests. If you are a multinational company storing data on a US-owned hyperscaler—even if that data is sitting in a local data center in Frankfurt, Tokyo, or São Paulo—you are exposed to profound legal conflict. A major data sovereignty violation can result in fines of up to 4% of your global annual revenue under frameworks like GDPR.
This is the primary driver behind the "Sovereign Cloud" movement. True data sovereignty requires more than just picking a geographic region on a cloud dashboard. It requires absolute control over the physical server, the hypervisor, the network routing, and the encryption keys. Partnering with localized bare-metal providers ensures that no foreign government can bypass international law to seize your intellectual property or customer data.
Mapping the Regulatory Landscape: A Global Breakdown
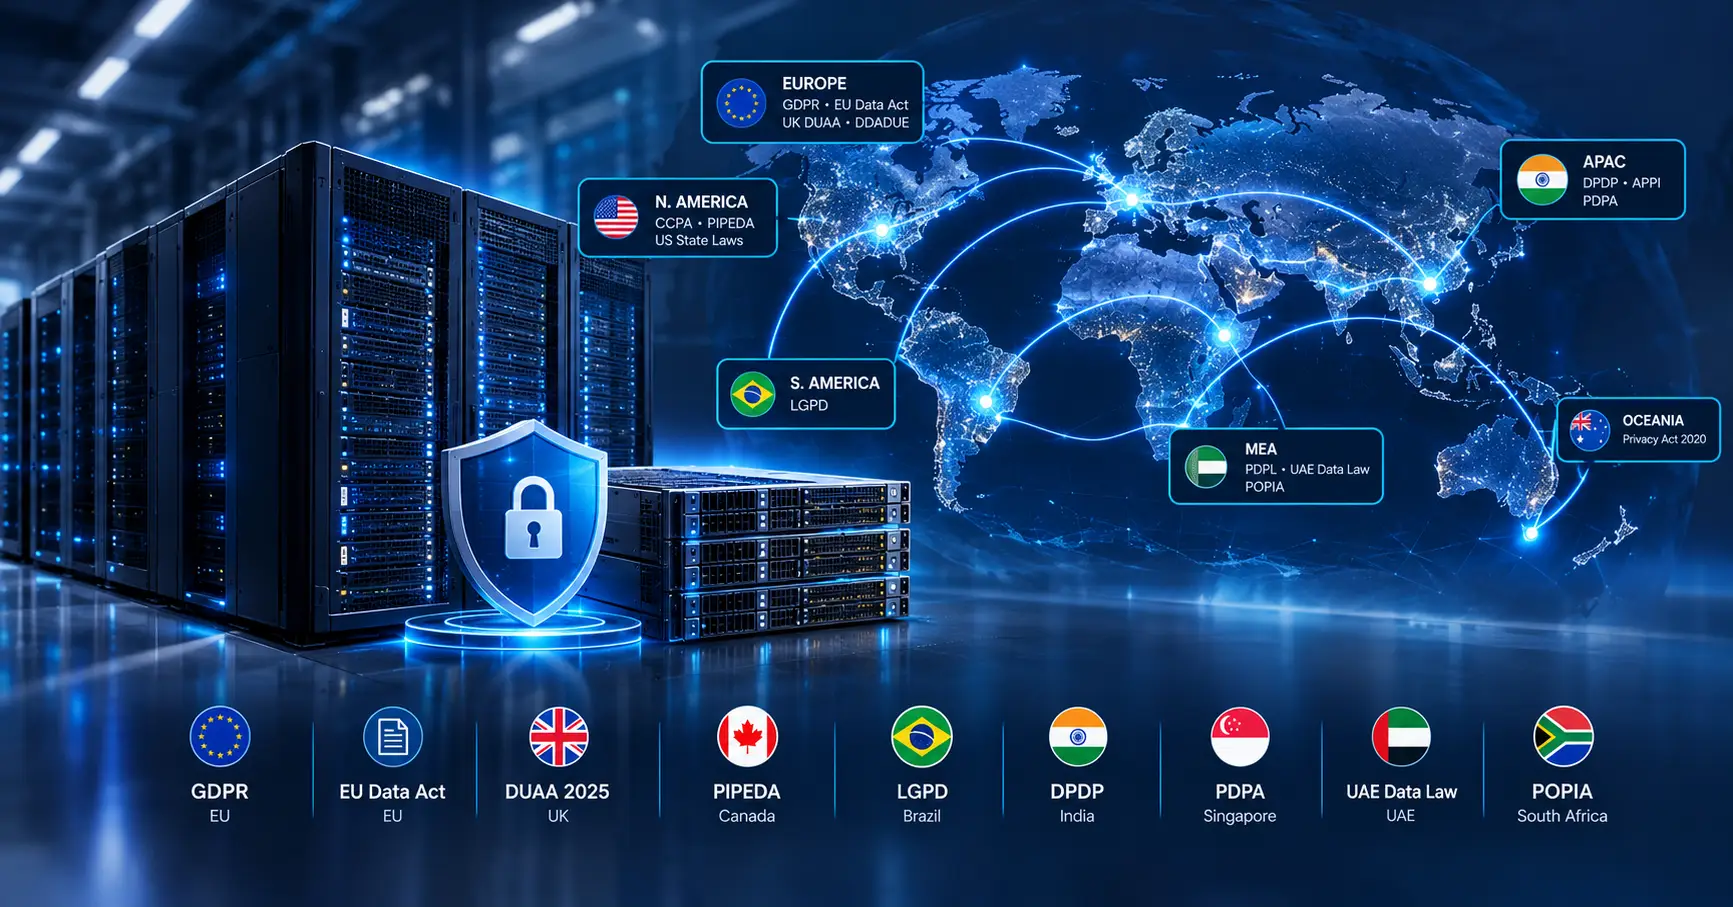
Data sovereignty is no longer just a European initiative. Across the Americas, Asia-Pacific, and the Middle East, nations are demanding that citizen and corporate data remain onshore. Managing a unified global digital service requires deploying physical hubs tailored to these specific regional frameworks.
UK DUAA & French DDADUE: The UK’s 2025 DUAA requires unique onshore logging, while France’s DDADUE mandates strict sustainability telemetry that only bare-metal hardware can accurately provide.
US Fragmentation: With varying state laws (like CCPA/CPRA in California), routing domestic data through central, controlled hubs ensures compliance across state lines.
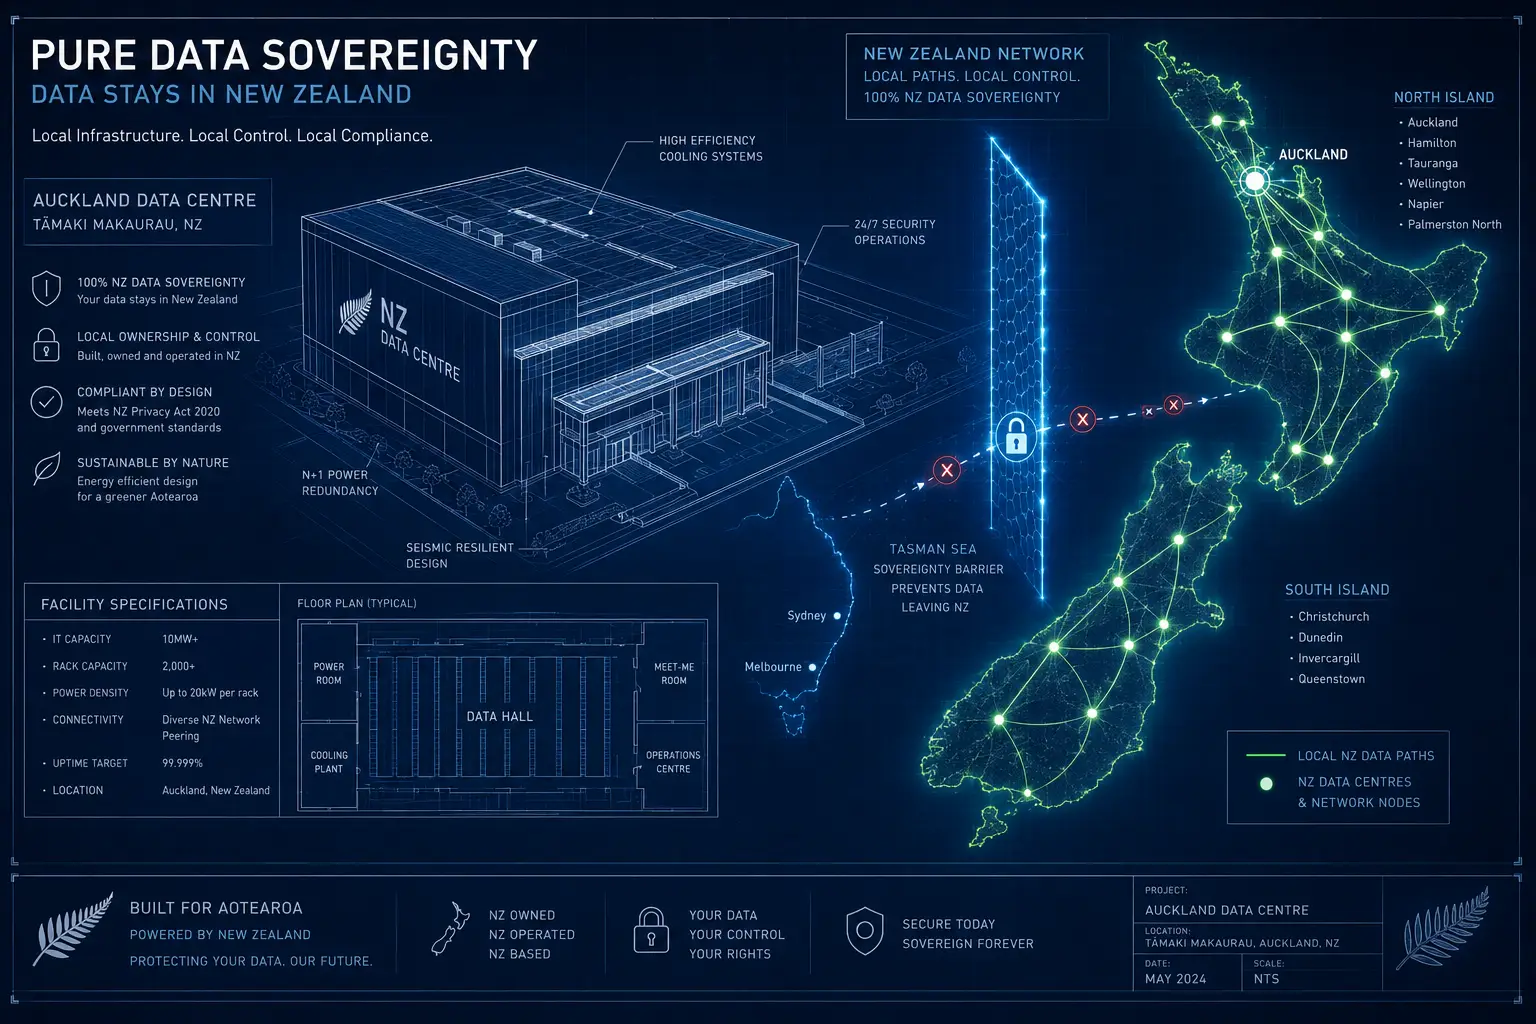
Trans-Tasman Isolation: Due to Australian surveillance laws, New Zealand mandates that its sovereign data (under the Privacy Act 2020) must be physically isolated in NZ, not routed through Sydney.
South Africa’s POPIA: The Protection of Personal Information Act limits data transfers to nations without matching adequacy agreements, requiring onshore African hosting for compliance.
Formulating a Sovereign Bare Metal Architecture
Achieving global data sovereignty requires transitioning from a centralized, generalized cloud strategy to a localized, dedicated infrastructure model distributed across continents.
The Verdict: Erasing the Compliance Burden
The age of unchecked global data fluidity is over. As international privacy acts and digital market regulations continue to fracture the global internet, relying on abstracted, multi-national public cloud infrastructure is a massive strategic liability.
By embracing a global network of dedicated, single-tenant bare-metal servers, multinational enterprises can transform legal compliance from a continuous operational nightmare into a guaranteed, hardware-backed certainty. Own your hardware, control your routing, and secure your global sovereignty with iDatam.
Frequently Asked Questions
iDatam Recommended Resources
Hardware
Why Are Intel, AMD, and Ampere Dominating the CPU Market?
When we choose a CPU, we had a lot to consider. However, the landscape of CPUs is mainly dominated by a few key companies depending on the market segment. No matter what kind of CPUs you're looking for, here's a breakdown of how things evolved and where they stand today.

Hardware
What is ARM?
ARM (Advanced RISC Machines) is a widely used family of RISC architectures developed by Arm Ltd., known for its energy efficiency and scalability. Since its founding in 1990, over 180 billion ARM-based chips have been shipped, making it the leading processor family globally.
Hardware
A Complete Guide to RAID Configurations: Balancing Performance and Data Protection
This guide digs into the world of RAID configurations, examining their advantages, disadvantages, and ideal use cases, as businesses and individuals increasingly seek ways to optimize their storage solutions in a data-driven world.
Discover iDatam Dedicated Server Locations
iDatam servers are available around the world, providing diverse options for hosting websites. Each region offers unique advantages, making it easier to choose a location that best suits your specific hosting needs.